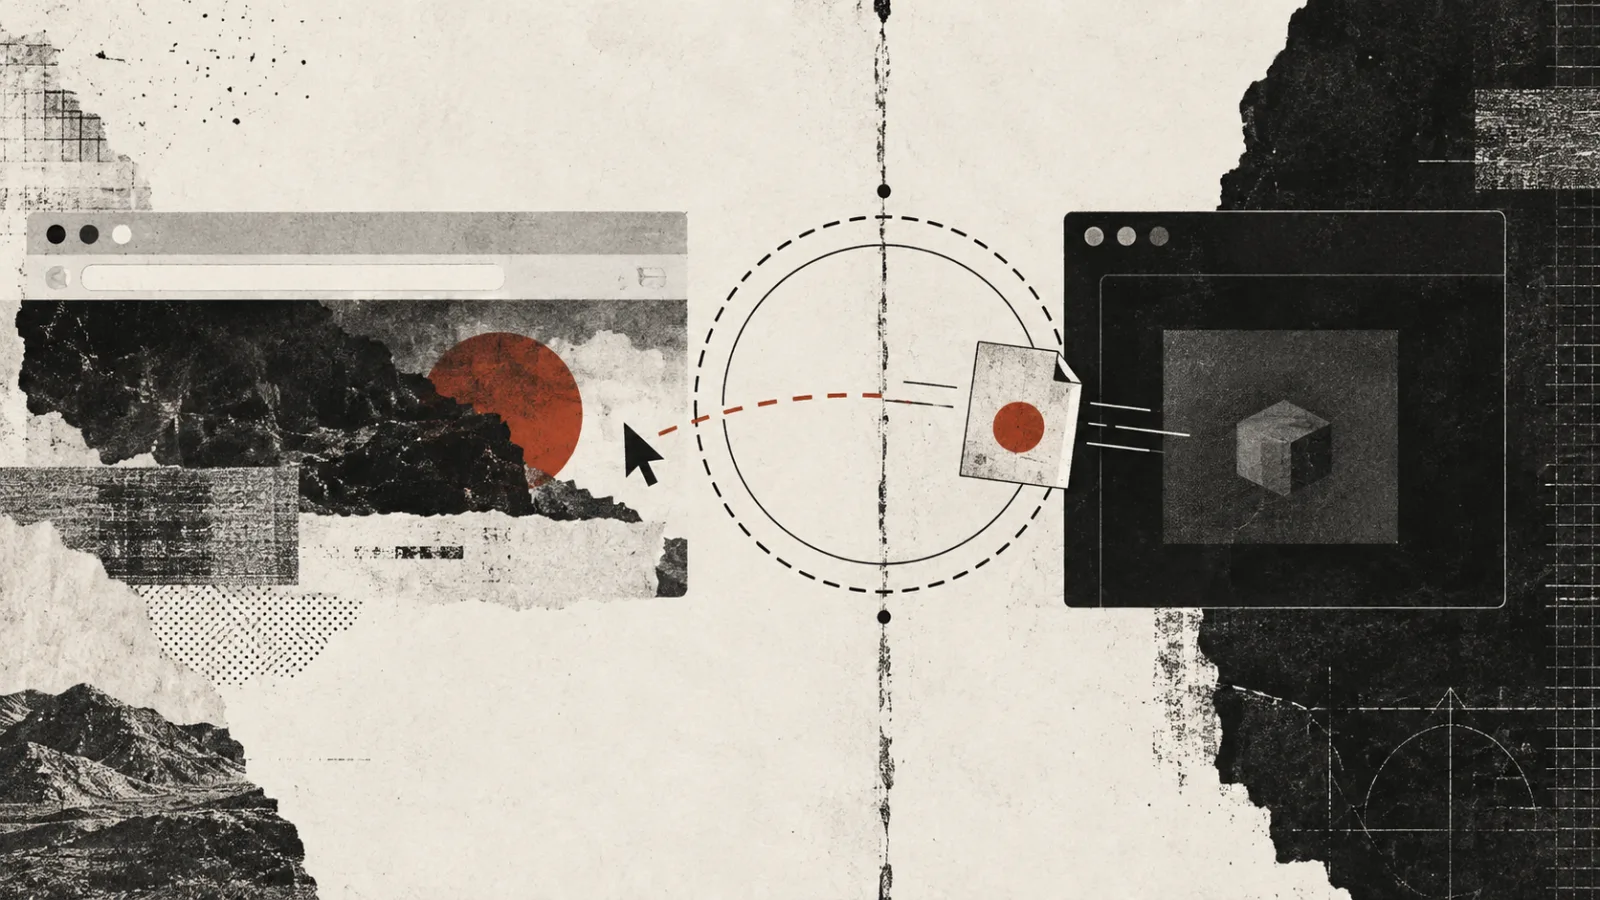
How visiting URL led to host RCE
A page searched a bounded localhost port range, found an unauthenticated editor socket, and planted a plugin that became one-click host code execution.
Experienced hackers lead every engagement. AI expands coverage and speeds up analysis, while human judgment validates every exploit, attack chain, and finding your engineers receive.
Independent research. Enterprise impact.
Security research recognized by Fortune 500 companies.
Vulnerabilities found and reported to
 Ubiquiti
 DataCamp
 BrowserStack
 Dell
 Matillion
 Bookipi
Reported through bug bounty and coordinated disclosure programmes.
Services
Every engagement is scoped to your system. You get a report your engineers can act on, and a retest once you have fixed things.
Multi-tenant platforms. Every role tested against every tenant.
BOLA, BFLA, mass assignment, and the endpoints your docs forgot.
The binary, and the backend it actually talks to.
Prompt injection, tool abuse, and the blast radius afterwards.
IAM paths to privilege, and what one leaked key really reaches.
Perimeter and internal segments. What is exposed, and what chains.
Goal-driven. Tests whether anyone notices, not just whether a bug exists.
White-box, alongside the test. The bug classes traffic never surfaces.
Retest after your fix is included in every engagement, not billed separately.
Writings
A page searched a bounded localhost port range, found an unauthenticated editor socket, and planted a plugin that became one-click host code execution.
Who you work with
From scoping through retesting, experienced security practitioners stay directly involved. Every finding is validated, clearly documented, and discussed with your engineers. No layers of account management get between your team and the people doing the work.
confievil · co-founder
kxddah · co-founder
Ubiquiti
DataCamp
BrowserStack
Dell
Matillion
Bookipi
Contact
PGP [KEY FINGERPRINT]
NDA before scope, always.
We reply within [N] business days.